Ransomware accounted for 44% of publicly reported cyber incidents across the automotive sector in 2025, according to security firm Halcyon — attacks on
You can't patch OT like office IT. CISA now publishes ICS advisories almost weekly — dozens of vendors, hundreds of CVEs — but
Qilin ransomware is the most active group of its kind in the world in 2026 — more than 500 victim organizations, with manufacturing
Yes — manufacturing ransomware can shut a factory without ever touching a PLC. Dragos logged 1,140 industrial ransomware incidents in Q2 2026; 747
Internet-exposed PLCs are being actively targeted right now. If a PLC or HMI on your floor is reachable from the internet, assume it
When a vendor data breach exposes information you handed over, treat it as your own incident: confirm the scope in writing, inventory what
Freight invoice fraud is now the dominant threat in logistics billing: half of classified freight fraud is communication-based — fake invoices, compromised inboxes,
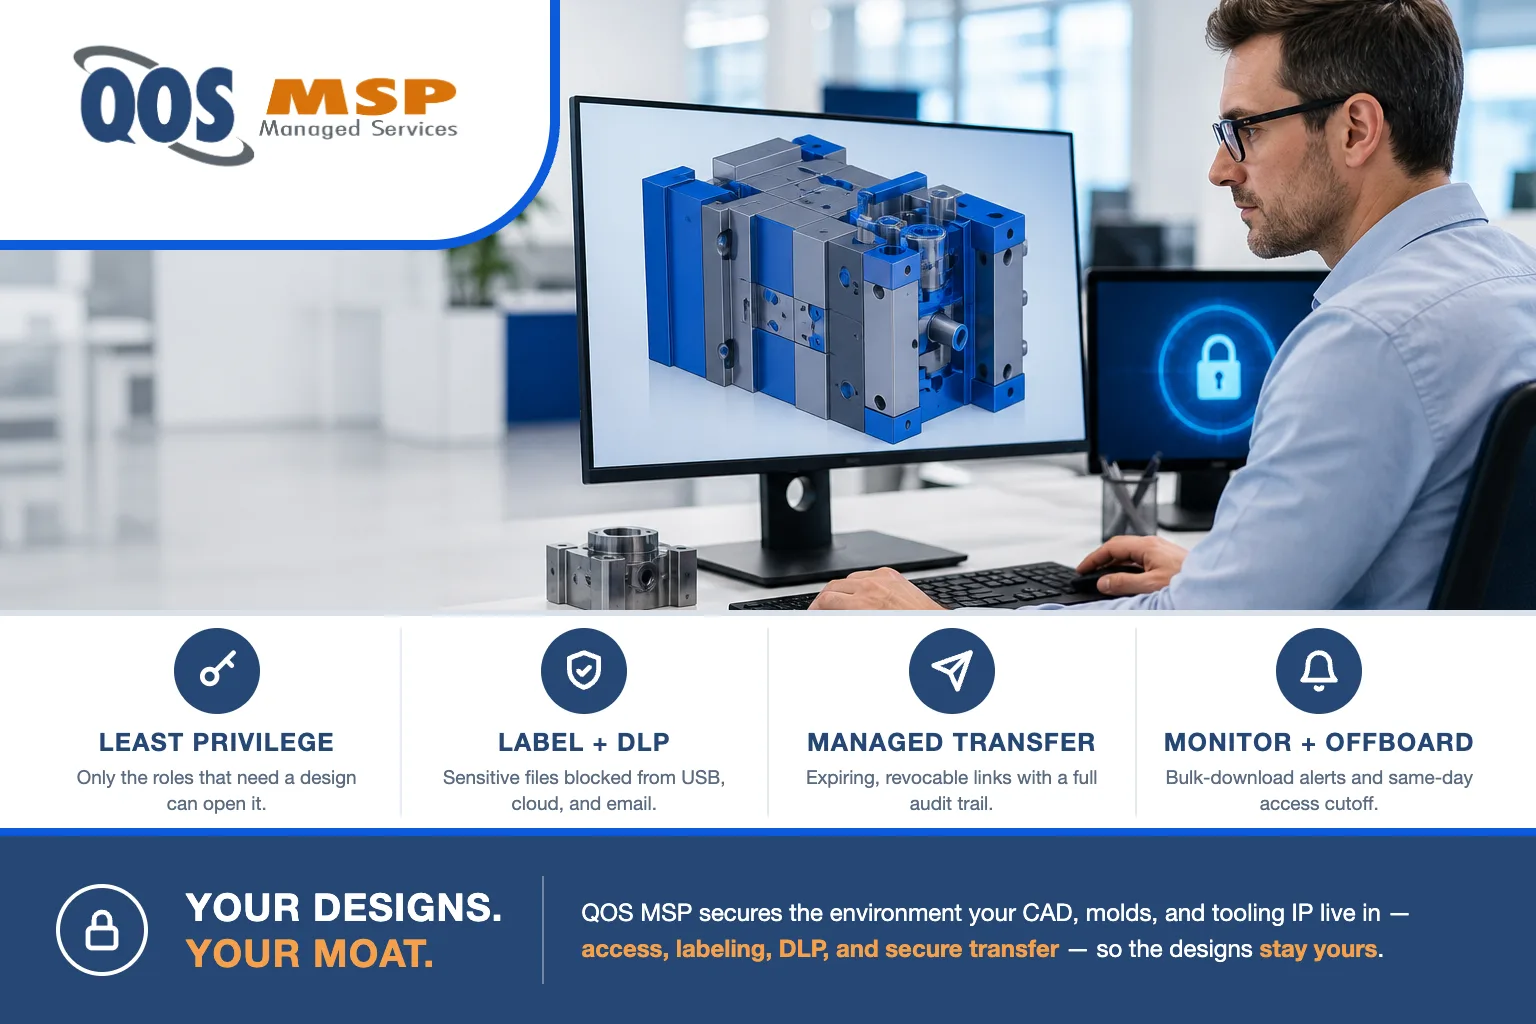
Learning how to protect CAD files, molds, and engineering IP starts with an uncomfortable fact: most stolen designs leave through ordinary channels —
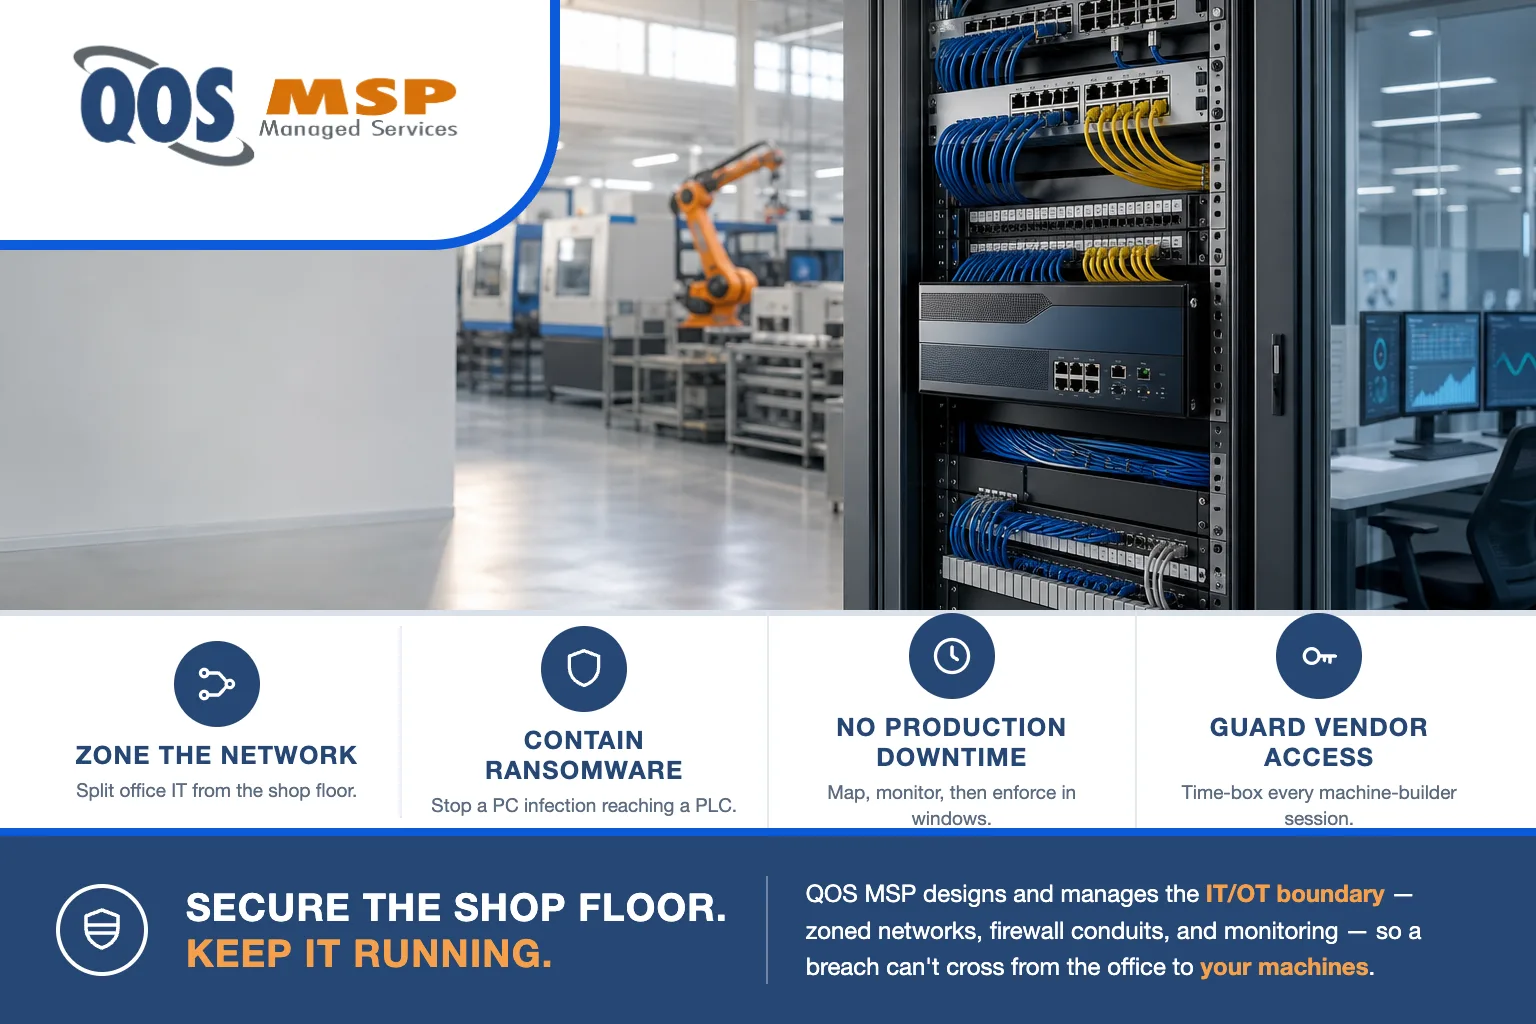
IT/OT network segmentation splits a manufacturing network into isolated zones — office IT, ERP, production/OT, legacy equipment, cameras, and guest — so ransomware
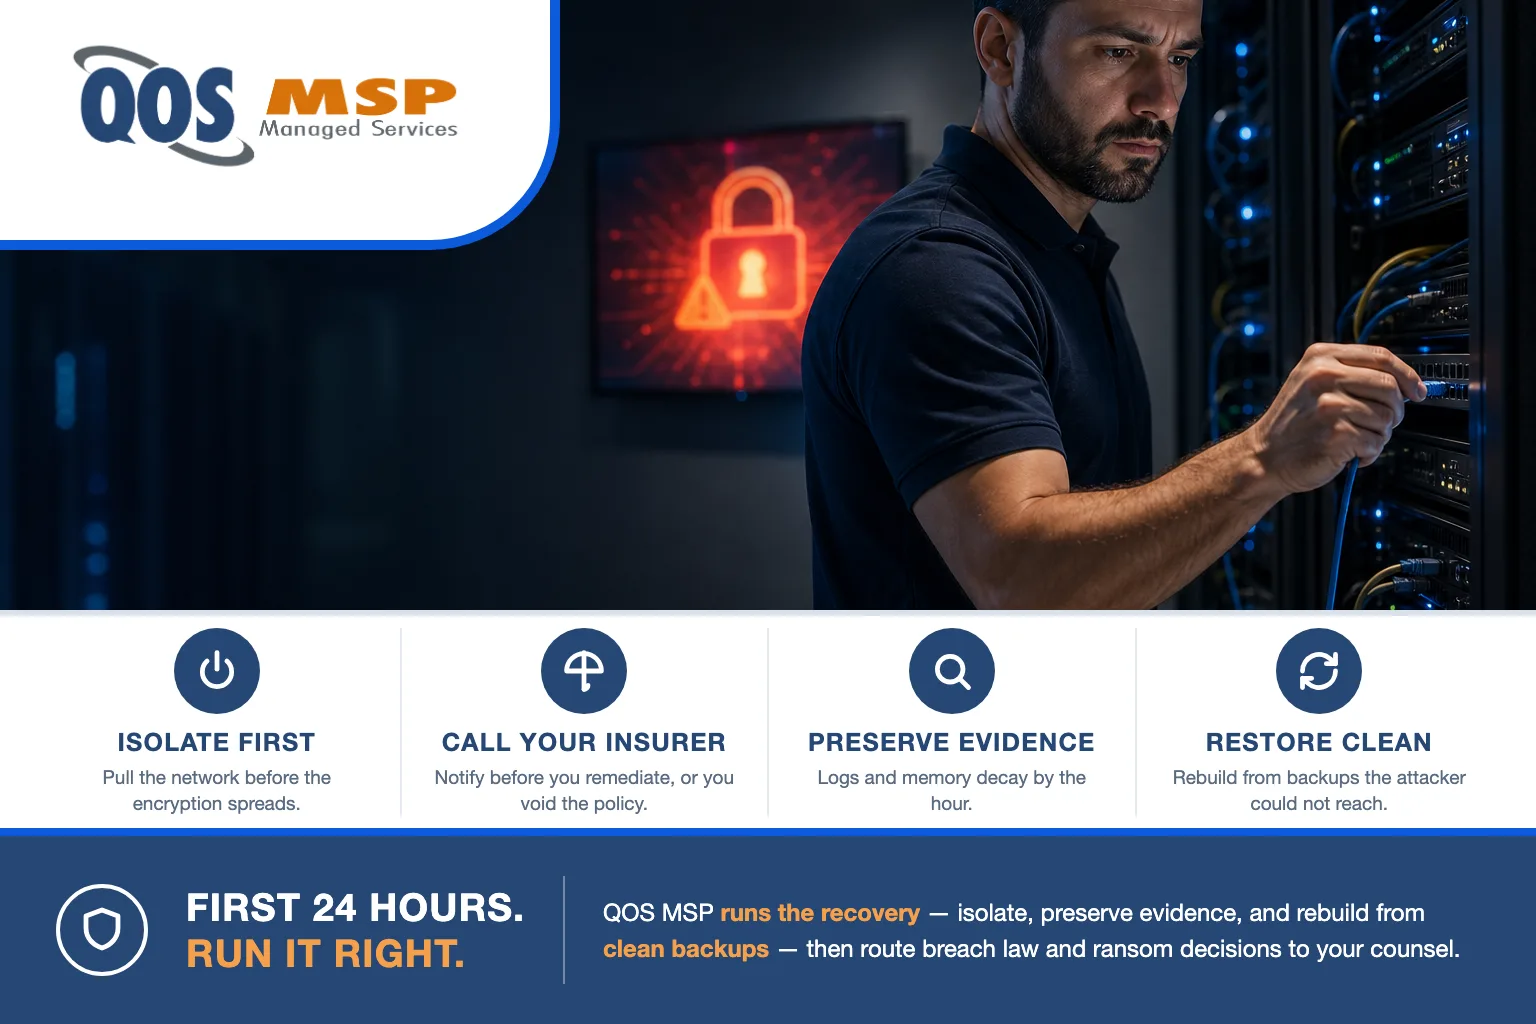
Knowing what to do after a ransomware attack comes down to one rule in the first minutes: disconnect infected machines from the network
- 1
- 2


<h5 class="widget-title mb-3">Recent Post