JLR Lost Five Weeks and £1.9B. What a Cyber Shutdown Actually Costs a Manufacturer
A cyberattack that stops production costs far more than the ransom. Jaguar Land Rover lost roughly five weeks of output,
Ransomware Is Now 44% of Automotive Cyberattacks — What a Dealer Group Actually Does About It
Ransomware accounted for 44% of publicly reported cyber incidents across the automotive sector in 2025, according to security firm Halcyon
CISA Ships an ICS Advisory Almost Every Week — How a Small Manufacturer Decides Which OT Patches Actually Matter
You can’t patch OT like office IT. CISA now publishes ICS advisories almost weekly — dozens of vendors, hundreds of
Qilin Is Now the #1 Ransomware Group Hitting Manufacturers and 3PLs — Here’s How It Gets In
Qilin ransomware is the most active group of its kind in the world in 2026 — more than 500 victim
Is Your Plant Floor on the Public Internet? What CISA’s New PLC Warning Means for Manufacturers
Internet-exposed PLCs are being actively targeted right now. If a PLC or HMI on your floor is reachable from the
Ransomware Hit 747 Manufacturers Last Quarter — Without Touching a Single PLC
Yes — manufacturing ransomware can shut a factory without ever touching a PLC. Dragos logged 1,140 industrial ransomware incidents in
CMMC Is Suspended — But NIST 800-171 Isn’t: What DoD Suppliers Still Owe
CMMC is suspended, not canceled. CMMC suspended still leaves every control in force. The Department of Defense (DoD) paused the
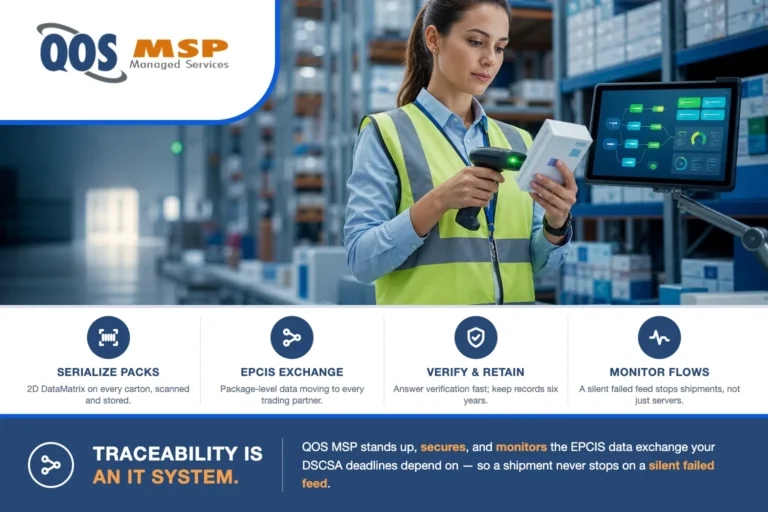
DSCSA Compliance in 2026: Why Drug Traceability Is Really an IT Project
DSCSA compliance is now an IT project: since August 27, 2025, wholesalers must exchange serialized, package-level EPCIS data electronically —
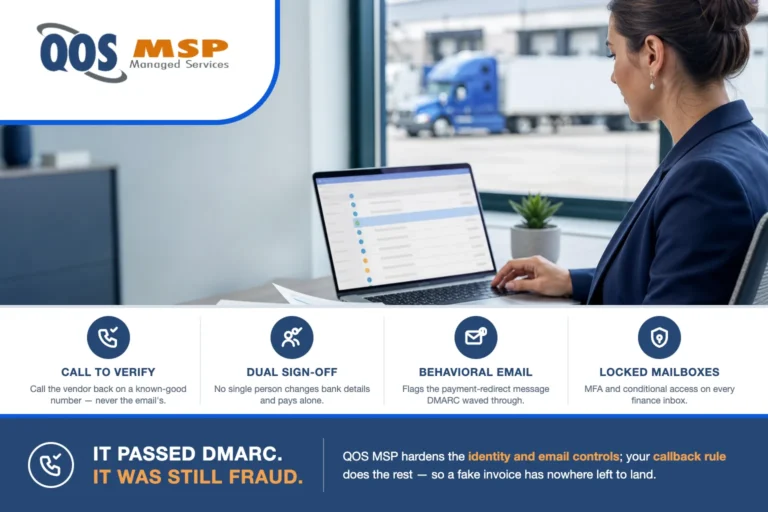
The Fake Freight Invoice That Passed DMARC — and What Actually Stops Invoice Fraud
Freight invoice fraud is now the dominant threat in logistics billing: half of classified freight fraud is communication-based — fake